[wp_tech_share]

Last week, I attended Cloudflare Connect 2026 in San Francisco as one of about 20 invited industry analysts. The most interesting story wasn’t an individual product announcement, but Cloudflare’s broader ambition to extend its global delivery and security network into infrastructure for AI agents that build, connect, and transact across the Internet. The opportunity is substantial because Cloudflare already operates at the intersection of several capabilities that could become increasingly important as machines assume a larger role in online activity.

Dell’Oro Group tracks Cloudflare across several security segments, including web application firewalls (WAF) and Security Service Edge (SSE). These security businesses remain important, but they may also provide the foundation for a broader developer and transaction platform.

Three observations from Connect illustrate both the strategic opportunity and the market implications worth watching.


The Internet’s Bodyguard Wants to Become Its Cashier

Matthew Prince, CEO of Cloudflare, highlighted a striking milestone during his keynote: Cloudflare data shows agentic AI traffic overtook human traffic in May 2026. That crossover arrived more than a year ahead of his original forecast, underscoring how quickly the Internet’s usage patterns are changing. Increasingly, the Internet serves two audiences: people who consume content and AI agents that retrieve information, interact with applications, and complete tasks on their behalf. This shift has implications that extend well beyond the volume of AI agent traffic.

AI agents place different demands on infrastructure because they can generate large numbers of requests, execute multistep workflows, and interact with services without direct human involvement. They also introduce questions about identity, authorization, and accountability, particularly when an agent acts on behalf of a person or organization. Cloudflare sees an opportunity at this intersection of networking, security, identity, and execution, building on a globally distributed network that already delivers applications and enforces security policies. Extending those capabilities into agent identity, execution, and payments could establish Cloudflare as an important infrastructure provider for the agentic Internet.

One particularly interesting opportunity involves the economics of agent-driven commerce. The Internet’s traditional business model has depended heavily on human visits, advertising, and referrals, but AI agents can consume content and computing resources without generating the traffic or revenue that previously supported content creators. Cloudflare’s Pay Per Use and Monetization Gateway initiatives seek to address this imbalance by enabling content and service providers to receive compensation when agents consume their resources. The direction is sensible, though it raises questions about how Cloudflare will set access, pricing, and payment terms as it increasingly mediates transactions between agents and content owners.

The opportunity extends beyond protecting existing business models and points toward a potentially significant category of machine-to-machine commerce. Cloudflare’s network reach naturally positions it to facilitate these interactions, while its existing security capabilities provide a strong foundation for building trust. However, interoperability, transparent policies, and customer control will be essential if these services are to become widely adopted Internet infrastructure. The Internet’s bodyguard is applying for a second job as its cashier, and the rules governing that role will matter.


The Developer Platform Is the Quiet Expansion Engine

The second observation is that developers, not solely enterprise security buyers, are increasingly pulling Cloudflare’s expansion. Workers, data services, and AI-related tooling allow developers to build and deploy applications without assembling conventional cloud infrastructure. Cloudflare OS extends that concept into an AI workspace that connects enterprise systems, selects models, and orchestrates workflows using Cloudflare’s underlying services. Together, these capabilities suggest Cloudflare wants to become an increasingly natural destination for AI-era applications.

The commercial logic is worth examining because the adoption model differs from traditional enterprise software. An open-source workspace does not necessarily generate direct licensing revenue, but applications built around it can increase consumption of compute, data, identity, security, and AI gateway services. A developer begins with a useful application, and the enterprise gradually inherits a broader infrastructure relationship as that application moves toward production. The opportunity is attractive for Cloudflare, although the durability of this consumption model will depend on how successfully experimental workloads become business-critical applications.

Two customer examples illustrated the potential. Block, the financial technology company behind Square and Cash App, described using Cloudflare to incubate employee-created applications without disrupting production systems, while consolidating workforce access under a consistent Zero Trust architecture. The developers at Block were instrumental in picking Cloudflare’s SSE/ZTNA solution. Montclair State University demonstrated another compelling use case: using AI to create connective tissue across disparate enrollment, housing, financial aid, academic, and campus systems. Instead of forcing students to navigate multiple portals and piece together information themselves, an AI-powered workspace can bring those systems together to answer questions, identify next steps, and help students complete tasks. Both examples show how AI can unlock value from existing enterprise systems without replacing them.

The major hyperscalers—Amazon Web Services (AWS), Google Cloud, and Microsoft Azure—are unlikely to lose their central role, especially where databases, long-running workloads, and compliance requirements create substantial inertia. Enterprises may nevertheless welcome Cloudflare for distributed execution, application integration, and security while retaining their core data and systems in hyperscaler or private clouds. However, infrastructure lock-in remains a concern, even when the application framework itself is open source, because operational dependencies can accumulate around the underlying infrastructure services. Cloudflare’s opportunity may be to win more of the work between clouds rather than displace them.


AI Makes Security More Important—and Changes Its Economics

The third observation matters for cybersecurity markets because AI is expanding the attack surface while improving security teams’ productivity. AI accelerates application development, increases API activity, and introduces autonomous agents that can take action, creating additional demand for security controls. At the same time, AI-assisted engineering, vulnerability discovery, investigation, and remediation could reduce the labor required to achieve security outcomes. The resulting dynamic is important: increasing cyber risk does not necessarily translate into proportionately higher spending across every security product category.

Application security provides a useful example because faster software development creates both advantages and difficulties. AI-assisted coding can boost development productivity and potentially reduce certain classes of vulnerabilities, but it also enables organizations to build more applications, APIs, and business logic that need protection. Even well-written code cannot prevent every inappropriate action, particularly when an AI agent executes a legitimate API request for a purpose its user never intended. Consequently, security increasingly needs to evaluate identity, authorization, application context, and permissible actions rather than relying exclusively on identifying known exploits or malicious requests.

This evolution plays to Cloudflare’s strengths in distributed enforcement because its network provides a common infrastructure for applying security policies close to applications and users. Combining these capabilities with agent identity, application execution, and AI governance could create meaningful differentiation as enterprises seek more coordinated security architectures. Customer presentations reinforced the practical importance of these capabilities: eBay described agentic tools supporting customer security operations and cybercrime intelligence, while Estonia demonstrated how centrally managed web and DDoS defenses can protect government services against sustained attacks. Neither example suggests that traditional security requirements are disappearing, but both illustrate how automation and shared enforcement infrastructure may change the economics of delivering security outcomes.

The broader implication is that AI could increase demand for security while also pressuring products whose primary differentiation rests on manual workflows, data aggregation, or basic orchestration. Vendors will increasingly need to demonstrate differentiated context, reliable enforcement, and operational accountability rather than simply adding an AI interface to existing products. For Cloudflare, this presents an opportunity to extend the value of its network and security capabilities into emerging AI workloads. For the cybersecurity market, it suggests that competitive advantage increasingly depends on how effectively vendors coordinate identity, application context, policy, and enforcement across distributed environments.


What I Will Be Watching

Cloudflare’s strategy now spans markets that enterprises have historically budgeted and managed separately, but the underlying capabilities increasingly reinforce one another. Its network provides global reach, security establishes trust, developer services generate workloads, and agent identity and payments introduce additional monetization opportunities. More developers create more applications, which generate traffic and require security, while growing agent activity increases the importance of authorization and transaction services. The strategic logic is compelling, although translating those relationships into sustained commercial growth will require continued execution.

I will be watching three developments as the strategy unfolds. First, can Cloudflare convert growing developer adoption into durable enterprise workloads that generate meaningful infrastructure consumption? Second, will agent identity, authorization, and payment capabilities mature into sufficiently open and interoperable services that enterprises can deploy them confidently? Third, can Cloudflare translate its expanding technology footprint into a coherent operating model that customers increasingly view as broader application and AI infrastructure rather than primarily security and delivery services?

For the cybersecurity industry, the implications reach beyond Cloudflare because AI is accelerating the convergence of networking, application delivery, security, and distributed computing. Vendors that can coordinate these capabilities will capture larger shares of enterprise infrastructure spending, although the economics of individual product categories could evolve considerably along the way. My takeaway from Connect is that Cloudflare is no longer simply asking how much more of the security stack it can address; it is asking how much of the agentic Internet it can help operate. Security may be the on-ramp, but what matters next is whether customers trust—and pay for—the road beyond it.
[wp_tech_share]

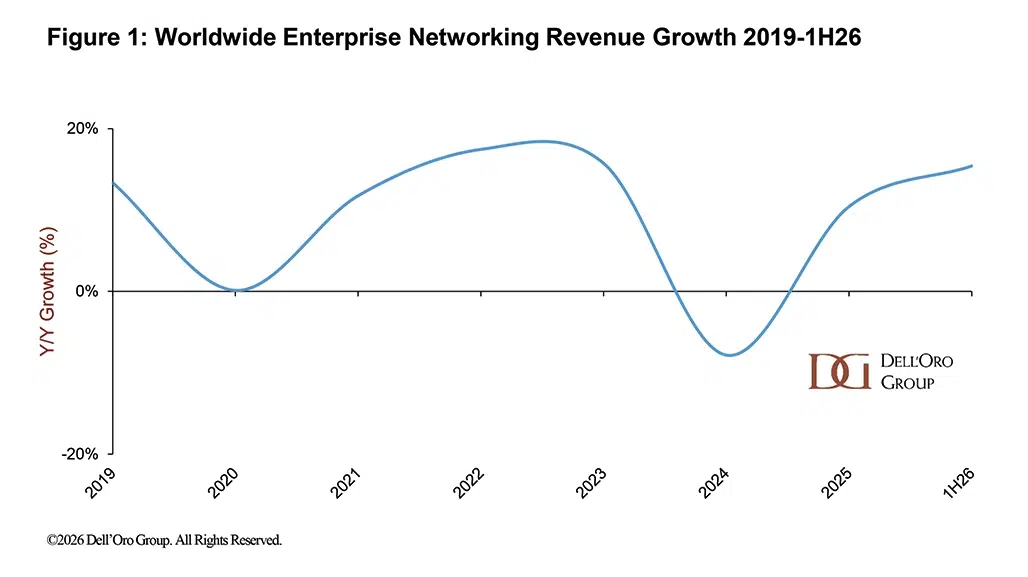
A year ago, we questioned whether the recovery in Enterprise Networking could sustain itself after several years of extraordinary market swings. The first half of 2026 has provided an encouraging answer. Worldwide Enterprise Networking revenue grew 15% year over year (Y/Y), with all five major segments—Network Security, Branch Routing, WLAN, Campus Switching, and Enterprise Data Center Switching—posting double-digit gains. Growth accelerated further in the second quarter.

Yet the headline figures conceal increasingly different market dynamics. Some segments are benefiting from rising equipment shipments, others from higher prices, and still others from changes in how enterprises connect and secure their infrastructure. Artificial intelligence (AI) is complicating the picture, generating new infrastructure requirements while also driving up the cost of traditional networking equipment. As the industry looks toward 2027, the central question is how much of the current expansion reflects durable investment demand and how much reflects pricing and purchase timing.


From Recovery to Expansion

The Enterprise Networking market has traveled a rocky road since the pandemic. Supply shortages and accumulated backlogs drove exceptional revenue growth in 2023, followed by a sharp correction as shipments normalized and enterprises worked through excess inventory. The market contracted in 2024 before returning to growth in 2025 (Figure 1). With the inventory digestion behind us, enterprise spending has entered a new investment cycle shaped by technology refreshes, security modernization, rising prices, and shifting infrastructure economics.

WW Enterprise Networking Revenue Growth 2019-1H26 Dell'Oro Group

WLAN led the five markets in growth during 1H26, while Network Security contributed the most incremental revenue. Campus Switching, Branch Routing, and Enterprise Data Center Switching also expanded at double-digit rates, but their underlying drivers were far from uniform. In 2026, renewed supply shortages and rising prices are intersecting with genuine deployment growth and technology migration. Those forces will not necessarily persist on the same timetable.


When Revenue Growth Outpaces Underlying Demand

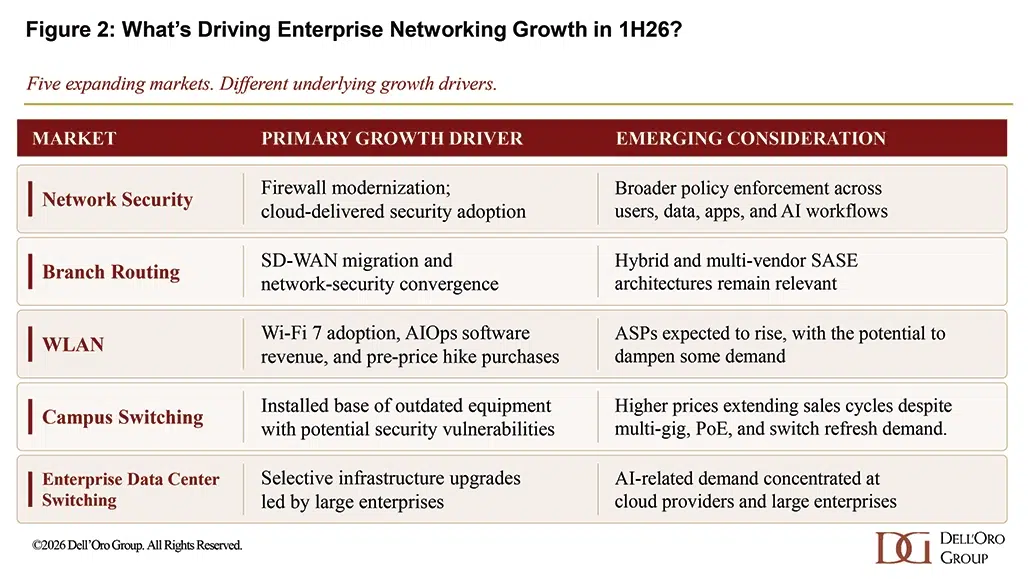
Campus Switching and WLAN illustrate the difference between stronger spending and stronger equipment demand (Figure 2). Campus Switching revenue grew at a double-digit rate in 1H26 even though port shipments were nearly flat following elevated shipment growth in 2025. Higher campus switch prices are now flowing through to vendor revenues; in 2Q26, port shipments fell 5% while ASPs surged 19%. Despite the large volume of end-of-support campus switches in the field, higher spending did not translate into a comparable increase in switch port shipments.

DDR4 memory shortages are a major source of pricing pressure, with memory costs escalating as AI infrastructure buildouts have tightened component supply. Enterprise IT vendors have raised prices, redesigned products, and sought alternative sources. Since enterprise equipment is often quoted well before delivery, these increases take time to appear in reported revenue. The latest Campus Switch results suggest that earlier price actions may be squeezing IT budgets and making some refresh projects harder to justify.

In 1H26, WLAN followed a different trajectory from Campus Switching, with revenue growth supported by higher access point shipments as Wi-Fi 7 adoption accelerated and enterprises ordered ahead of anticipated price increases. Wi-Fi 7 now accounts for most indoor access point revenue. Vendors are also contending with DDR4 memory shortages, which we expect will push WLAN equipment prices higher in 2H26. Meanwhile, recurring software licenses and advanced AIOps capabilities are becoming increasingly important revenue sources in a market historically dominated by hardware sales. Together, these developments are changing both the economics of WLAN deployments and how vendors monetize their installed bases.

Enterprise_Networking_Growth_Matrix_1H26-1

AI Is Both a Tailwind and a Headwind

AI infrastructure investment has been a strong catalyst for the broader Data Center Switching market, particularly among hyperscalers and specialized cloud providers building networks for training, inference, and agentic workloads. Enterprise demand is more measured. Growth in enterprise front-end Data Center Switching has been concentrated among large organizations, often as part of upgrades to networks supporting general-purpose servers rather than dedicated AI deployments. Smaller enterprise customers have continued to pull back on purchases.

Many enterprises are still deciding where AI workloads should run and whether the expected benefits justify new on-premises infrastructure. Public cloud services offer an alternative to owning compute and networking equipment. Meanwhile, the AI buildout is tightening supplies of components also used in campus and wireless networks. It can therefore lift traditional networking revenue through price increases even where AI is not generating incremental equipment demand. Higher costs could, in turn, encourage customers to extend product lifecycles or redirect budgets.

AI is also expanding security and operations requirements, from protecting sensitive data and governing AI applications to managing non-human access and defending against more capable attackers. Much of the near-term commercial opportunity is being captured through capabilities added to established platforms rather than entirely new product categories. For now, network modernization, risk reduction, and operational efficiency remain more tangible purchasing drivers than broad AI-led replacement cycles.


Cybersecurity Becomes a Modernization Catalyst

Network Security was the largest contributor to Enterprise Networking revenue growth in the first half, supported by targeted Firewall refreshes and continued adoption of cloud-delivered security. Within Security Service Edge (SSE), separately monetized Data Security and Digital Experience Management capabilities are expanding faster than foundational access and inspection. Enterprises are extending security policy across users, applications, data, and workloads, with AI introducing additional requirements rather than replacing existing ones.

Cybersecurity concerns are increasingly influencing spending beyond security products. Aging switches, routers, and wireless access points have always needed replacement as performance requirements rise or vendor support expires. Now, vulnerability exposure and concerns about AI-assisted cyberattacks are making those refresh decisions more urgent. Channel discussions suggest that security audits are identifying unsupported equipment and initiating replacement projects. Infrastructure modernization is becoming as much a resilience decision as a capacity decision.

The shift is especially visible in Branch Routing, where SD-WAN continues growing while traditional Access Router revenue contracts. Enterprises are using router refreshes to adopt software-defined connectivity and integrate networking with cloud-delivered security through Secure Access Service Edge (SASE). The result is not necessarily a single-vendor architecture: operational maturity, existing investments, and sovereignty requirements still favor hybrid or multi-vendor approaches in many environments. Network management is evolving similarly. Cloud-managed Campus Switching is outpacing the broader market, but premises-based and private-cloud WLANs remain important, reflecting the trade-offs among automation, recurring fees, and control.


Which Way Are We Headed?

We remain optimistic about Enterprise Networking, although growth is likely to moderate from the first-half pace. Wi-Fi 7, installed-base refreshes, security requirements, and SD-WAN adoption provide durable support. Countering those tailwinds are component shortages, higher equipment prices, and purchasing pull-forwards that may dampen subsequent shipments even if modernization plans remain intact.

As 2027 approaches, we will be watching whether equipment demand can withstand higher prices, whether AI investment spreads beyond cloud providers and the largest enterprises, and whether automation and cybersecurity investments deliver the operational benefits buyers expect. Sustaining market expansion will increasingly depend on the underlying need to modernize rather than on higher prices or shifts in purchase timing.

[wp_tech_share]

I attended Mplify’s member summit in Boston several weeks ago, where I also served as a judge for its NaaS awards. One theme stood out: enterprise networking and security are becoming more integrated, yet delivering that integration across the broader communications service provider industry remains surprisingly difficult. Technology providers are combining capabilities enterprises historically bought separately, while communications service providers are working to make their networks and operational systems function as a coordinated ecosystem.

Both efforts are moving toward the same objective: making enterprise networking and security simpler to consume and operate. In my Distributed Cloud Networking (DCN) research at Dell’Oro Group, this tension is becoming increasingly important. The question is not whether Network-as-a-Service (NaaS) will evolve beyond connectivity. It already is. The more interesting question is whether the industry can deliver an integrated experience without forcing enterprises to rely on a single technology provider.

Four observations from Boston stand out.
The Networking and Security Stack Is Converging, but Innovation Is Far from Over

In my DCN research, I look at the enterprise WAN through three interconnected domains: the user/WAN edge, WAN middle mile, and cloud/application edge. Each has traditionally been served by different technologies and vendors. SASE and SD-WAN address secure user and branch connectivity, WAN-as-a-Service brings greater flexibility and programmability to the middle mile, and multi-cloud networking extends connectivity and security controls closer to distributed applications and workloads.

The boundaries between these domains are becoming less rigid. Convergence is happening horizontally as providers extend their capabilities across the three domains, and vertically as networking, security, observability, and automation become more tightly integrated. For some enterprises, this creates an opportunity to collapse a complicated networking and security stack into a more unified operating model, with fewer control planes, fewer integration points, and more consistent policy enforcement.

However, convergence should not be mistaken for the end of specialization. Significant innovation continues within each domain, and some of the more interesting developments are happening outside the traditional SASE conversation. The WAN middle mile, for example, is gaining renewed importance as enterprises look to dynamically connect private data centers, public clouds, AI factories, and emerging neocloud providers. At the cloud edge, application-aware networking and security continue to evolve, while SASE vendors are extending beyond traditional user-to-application traffic into broader infrastructure use cases.

AI is accelerating these developments, but it did not create the underlying challenges. Cloud adoption, distributed workforces, and application decentralization were already reshaping enterprise networking. AI adds urgency through more dynamic workloads, distributed inference, and new requirements for data governance and security. The important takeaway is that the market is still innovating within individual domains even as the broader technology stack converges.


Two Paths Toward a Simpler Enterprise Experience

One response to these market dynamics is technology convergence. Providers are extending their capabilities across traditional product boundaries to deliver more networking and security functions through a common platform. The appeal is understandable: enterprises increasingly want consistent policy, visibility, and operational control across users, branches, cloud environments, and applications. A more integrated provider can potentially reduce the complexity of making those pieces work together.

However, there is another path: a federated ecosystem of specialized technology and service providers. Not every enterprise wants to standardize on one vendor, nor will one vendor necessarily deliver the best capabilities across every domain. Existing investments, geographic requirements, specialized security needs, and heterogeneous application architectures will continue to create demand for best-of-breed solutions. The challenge is making those independent technologies behave like a coordinated service rather than a collection of individually managed products.

I do not see these approaches as mutually exclusive. Even highly integrated platforms depend on third-party connectivity and infrastructure to extend their reach. Likewise, a multi-provider ecosystem can offer customers a unified experience if the underlying integration is mature enough. This creates an interesting competitive dynamic: innovation within individual domains remains valuable, but the ability to integrate and operationalize those technologies becomes equally important.

In that sense, the real competition is not simply single-vendor versus multi-vendor. It is about which approach can deliver the required capabilities with the least operational friction, while preserving the flexibility enterprises need as their architectures evolve.


Boston Highlighted the Gap Between Federation and Execution

Federation was one of the strongest themes throughout Mplify’s Boston event. There was broad agreement that no single service provider can deliver every component of a global enterprise network, particularly as cloud and AI workloads become more geographically distributed. More importantly, several presentations showed that industry collaboration is moving beyond architecture diagrams into practical commercial workflows.

Bob Victor, Comcast Business’s Chief Product Officer and Mplify Board Chair, discussed efforts to connect Comcast and Colt’s automated workflows. Both companies have invested in internal automation, but transactions between them have historically involved spreadsheets and manual handoffs. Verizon described its use of Mplify’s Lifecycle Service Orchestration (LSO) Sonata APIs for wholesale transactions and its direction toward replacing legacy Access Service Request processes with standardized interfaces. Equinix and Comcast also discussed efforts to simplify service discovery and connectivity procurement through interconnected marketplaces.

These developments stand out because they show progress toward making independently operated networks function as a coordinated supply chain. However, the discussions also exposed a significant maturity gap between today’s implementations and the vision of fully automated, federated networking. Automating service discovery and quoting is not the same as automating end-to-end delivery. A provider may return a quote in seconds while installation, provisioning, troubleshooting, and performance assurance still depend on manual processes.

Legacy OSS/BSS environments, inconsistent operational data, and limited automation among smaller partners remain obstacles. There is also a commercial dimension that received welcome attention in Boston. Standardized interfaces do not automatically resolve contractual complexity, layers of reseller margin, service-level accountability, or ownership of the customer relationship. These are not secondary issues. They directly affect whether a multi-provider solution can compete with the simplicity an integrated platform promises.

This was one of my biggest takeaways from Boston. Federation requires business-model innovation alongside technical interoperability, and the industry still has considerable work to do on both fronts. The opportunity is significant, but getting multiple providers to communicate is only the first step toward making them operate as one.


Standardization Is Becoming More Important, Not Less

Having participated in standards efforts at the IETF and Trusted Computing Group, I appreciate the work required to build industry consensus and turn technical specifications into interoperable implementations. Standards do not eliminate competition or technological differentiation. Done well, they provide a common foundation on which companies can innovate without forcing customers into proprietary integration models.

This is why I view Mplify’s work as strategically important. The alliance has spent years developing Carrier Ethernet service definitions, LSO APIs, common product models, and certification programs. These assets are increasingly relevant as enterprises seek cloud-like consumption models across multiple communications service providers. Standardization also creates an opportunity for smaller and specialized providers to participate in larger ecosystems without having to build custom integrations for every commercial relationship.

Now Mplify is extending that work toward agentic automation and federation. Its LSO framework now supports the Model Context Protocol (MCP), and ongoing initiatives are developing reusable AI-agent capabilities, trusted provider discovery, and agent-to-agent coordination. The direction is promising because it builds on the existing service definitions, data models, and transaction workflows rather than assuming AI agents can independently solve the complexities of network operations.

In fact, AI may increase the importance of standardization. An agent that can discover and order connectivity is useful, but an agent that can reliably coordinate those actions across multiple providers while respecting commercial agreements, workflow sequencing, and security policies is far more valuable. Achieving that requires common definitions of services, authorization, operational states, and expected outcomes. It also requires mechanisms to verify that the agents and underlying systems behave as intended.

The industry is not there yet. The agentic federation vision remains ahead of broad production adoption, and considerable work remains on conventional service automation. Still, I see the effort as directionally constructive. The challenge for Mplify and its members will be translating the standards and architectural work into repeatable implementations that deliver measurable improvements in service delivery and operational efficiency.


What I Will Be Watching

The next phase of NaaS will be shaped by two related developments. First, how far can technology providers simplify enterprise networking through horizontal and vertical integration? Continued innovation across the user edge, middle mile, and cloud edge will create new possibilities, but comprehensive technology coverage does not automatically translate into a coherent operating model.

Second, how quickly can the broader service provider ecosystem close the interoperability gap? Mplify’s standards and certification work can help, but success ultimately depends on adoption, operational integration, and commercial execution. The strongest evidence of progress will not be another architectural framework or federation demonstration. It will be the ability to consistently discover, order, deliver, secure, and assure services across multiple providers without pushing the complexity back onto the enterprise.

For enterprises, the outcome matters more than the architecture. Integrated platforms can absorb more of the enterprise networking and security relationship, while specialized providers can preserve their differentiation by becoming easier to integrate and consume. I expect both models to remain relevant, with competitive advantage increasingly determined by how effectively providers turn their technology and partnerships into a simpler customer experience.

Boston reinforced my view that the future of NaaS is not solely about who can assemble the broadest networking and security stack. It is also about whether the industry can make a network assembled from multiple providers operate with the simplicity and accountability enterprises increasingly expect from a single platform. That is the opportunity Mplify is helping the industry pursue, and it is where much of the next chapter of enterprise WAN innovation remains to be written.

[wp_tech_share]

Like a sailboat lying broadside to a supertanker’s wake, the Enterprise IT market is experiencing turbulence in the wash of massive AI infrastructure spending. With prices escalating, the LAN (Local Area Network) equipment market is already beginning to heel, and as the wake of the AI revolution spreads, more upheaval is on its way.

The first consequence of the trillions being spent on data center infrastructure is the shortage of available components left over for everyone else. Enterprise IT equipment, such as Wireless LAN (WLAN) Access Points and Campus Switches, is built using components that are not nearly as cutting edge and high performance as the ones that go into data center infrastructure for AI training. The IT market is facing shortages, nonetheless.


AI Infrastructure Spending Is Driving DDR4 Memory Shortages

Memory, in particular, has been front and center of collateral damage (see: The Growing Memory Tax on AI Infrastructure).  IT networking equipment uses an older generation memory (DDR4), but when the handful of memory producers shifted focus to the insatiable demand for High Bandwidth Memory for AI, DDR4 became hard to obtain, and therefore more expensive.

And “more expensive” seems like an understatement.

Over the past year, the spot price of DDR 8 Gbps memory chips has grown 788%. Vendors don’t usually pay spot prices, but this escalation demonstrates the kind of contract price pressures that systems vendors are facing.


WLAN and Campus Switch Prices are Growing as Memory Costs Escalate

Historically, memory was a small piece of IT equipment’s total cost to produce. For Campus Switches and WLAN, it was in the range of low-to-mid single digits of the total bill of materials.  But a component that represents 5% of the cost of a piece of equipment, and then grows in cost by 8 times, will increase the total cost of the equipment by 30%.

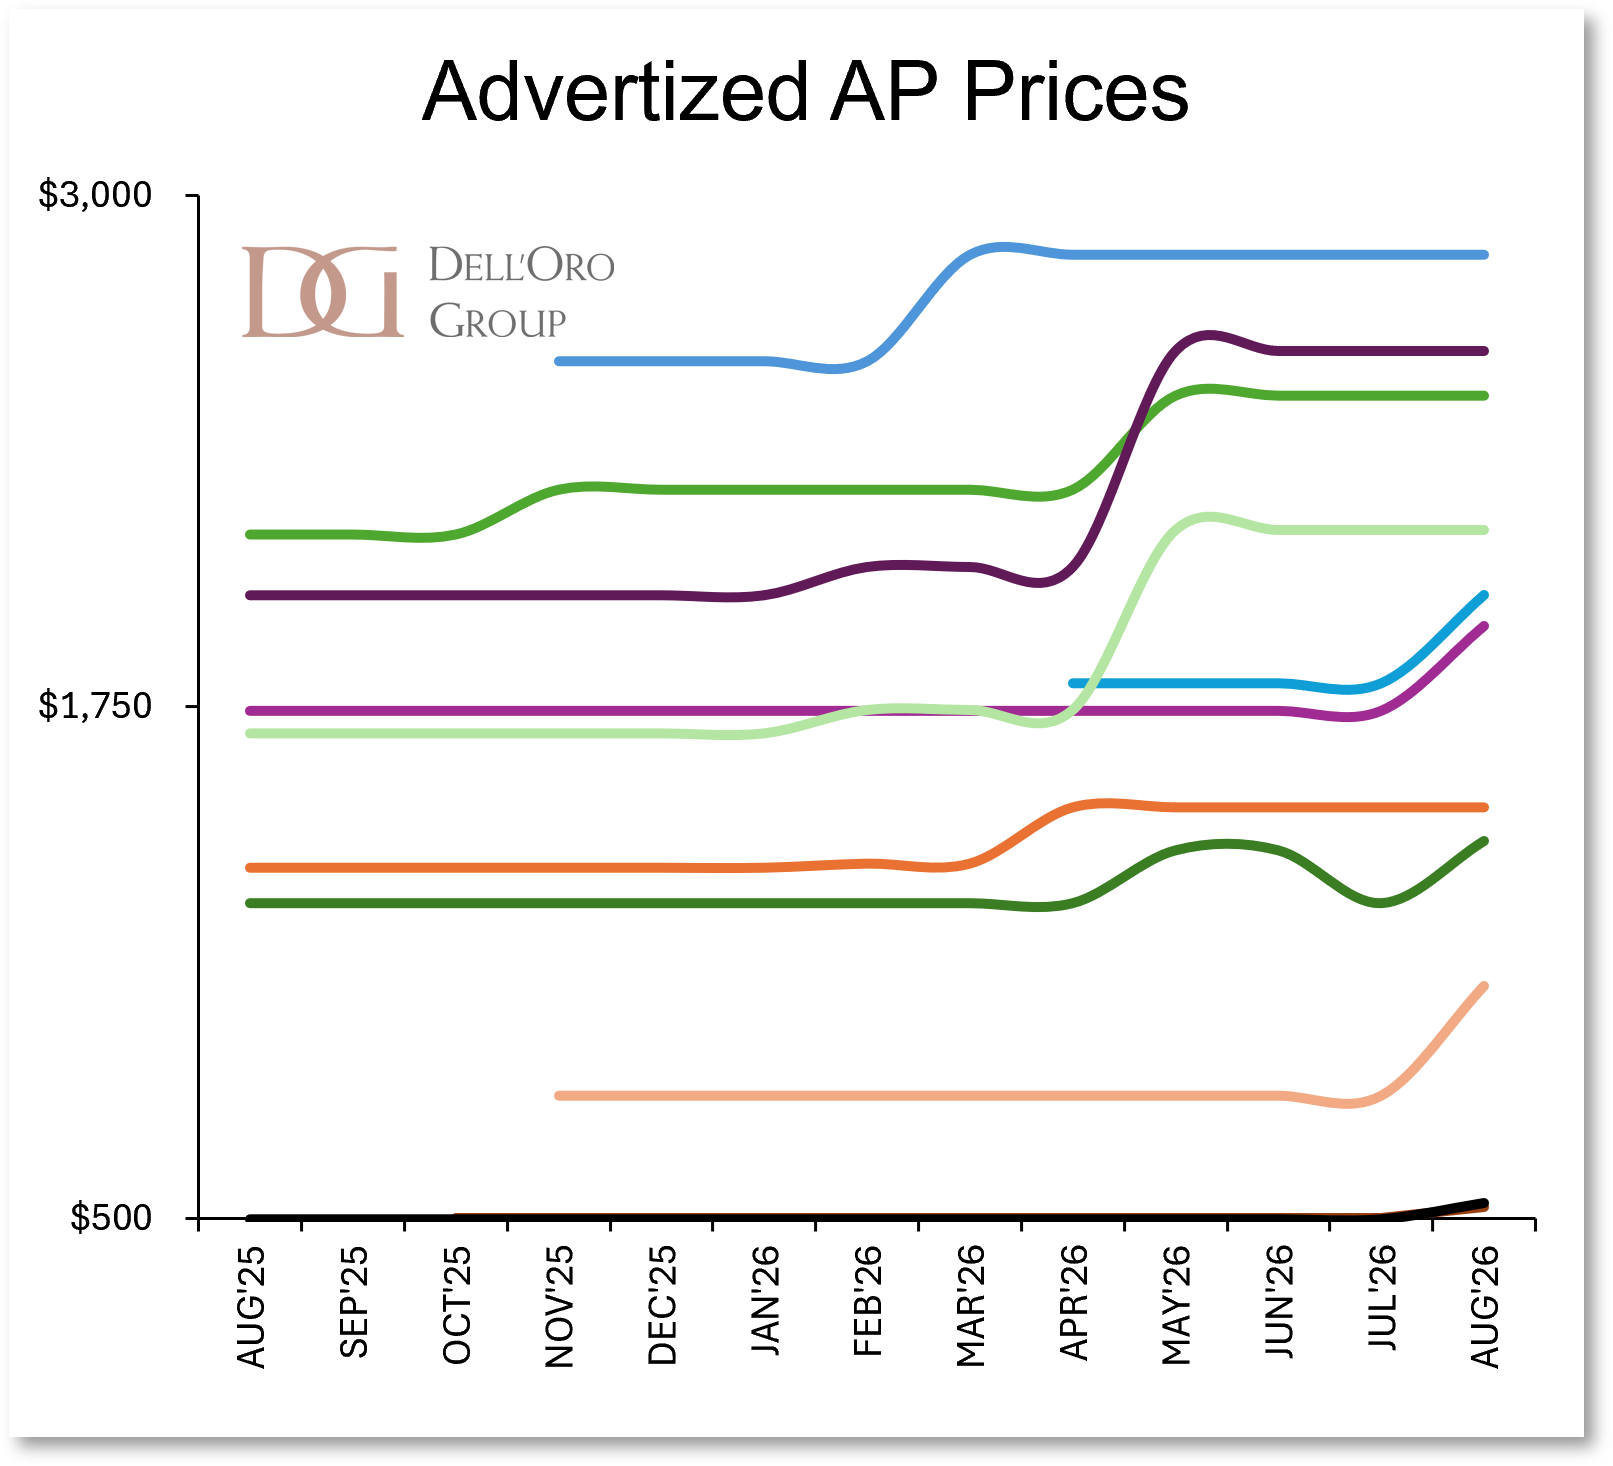
It is no wonder that nearly all WLAN and Campus switch vendors have increased prices at least once in the past year (some several times), as shown in a price graph of some of the most popular WLAN APs on the market.

Two years ago, WLAN or Campus Switch designs considered memory as a minor detail in the total cost equation, such that the equipment was not originally designed with memory efficiency in mind.  Even worse, in some cases, equipment was deliberately designed with more memory than required, to help make it future-proof and able to support yet-unknown applications.

Unfortunately, a simple swapping of one memory chip for a cheaper one inside a Campus Switch or WLAN AP is not as easy as it sounds. A new chip may involve a different board layout or power design; it may trigger firmware changes that would require regression testing.  A design change may necessitate new certifications in each market, adding costs and delays before a new product can be released.

This has left vendors scrambling to secure sources of memory in order to ensure a continued supply of APs and Campus Switches to the market. Lead times on some products have been variable, and vendors have shortened validity times for the quotes they issue, leaving them room to react to uncertain component pricing and availability.


Memory Shortages Are Expected to Shape the Enterprise LAN Market Until 2028

By 2Q26, most equipment vendors had reassured investors that sufficient memory supply has been secured for the next year or two.  However, supply shortages may still cause industry leaders some seasickness, and are likely to play out as follows:

  • Switch and AP prices are expected to rise even higher, although price growth should slow. With high levels of inflation affecting both DDR4 and DDR5, equipment prices are likely to remain elevated for several years.
  • Market demand could be suppressed. Although we have not witnessed any drastic downturns yet, it is common for enterprises to choose to wait to upgrade equipment or choose to take on smaller projects in order to avoid exceeding pre-established budgets.
  • Equipment lead times may continue to be uneven. Vendor terms and conditions (on returns, order cancellations, and quote price validity) are expected to remain tight.
  • Vendors may look for redesign opportunities, taking advantage of natural transition points (such as the introduction of Wi-Fi 8, or accelerated end-of-life dates) in order to deliver new, more memory efficient designs.

The return to some kind of memory supply-demand equilibrium is likely to occur as more memory-efficient equipment is released, and as more memory producers ramp up production.  These conditions are unlikely to be met before 2028.

Memory shortages are just one of the ways the LAN equipment market will be rocked by AI.  AI models are heightening cyber risks in the LAN, causing enterprises to perform security audits and focus on equipment patching and renewal.  Looking further ahead, once AI use cases are widely disseminated, there’s the possibility that LAN traffic patterns will change, leading to network redesigns. Under the pitch and roll of AI impacts, the IT industry will need to hold tight and focus on the horizon.

[wp_tech_share]

Last week, I was invited to attend Microsoft’s latest security launch, and it reinforced a central tension in enterprise cybersecurity: Agentic AI systems become more effective when they have deep access to telemetry, context, and enforcement controls. Yet the same integration that improves their effectiveness can also pull customers more tightly into one vendor’s platform.

Microsoft showcased four technologies at the launch event. Microsoft Perception is designed to coordinate security context, models, specialized agents, and enforcement mechanisms across Microsoft’s security estate. Red agents test environments, blue agents investigate threats, and green agents recommend or execute remediation. MDASH extends the architecture into source-code vulnerability discovery and developer workflows. MAI-Cyber-1-Flash provides a specialized model for part of that work, while Microsoft Security FORGE Labs will pursue more autonomous vulnerability discovery and remediation.

Microsoft’s potential advantage is the number of enterprise control planes it can connect. Defender supplies endpoint and security-operations context. Entra provides identity information. Azure contributes cloud context and enforcement. GitHub and Azure DevOps connect the system to source code and development workflows. A deeply integrated environment could allow an agent to move from a threat-intelligence question to an investigation, determine which identities and assets are exposed, apply a temporary control, and propose a permanent code fix. Context can be assembled before a model begins reasoning, potentially reducing ambiguity, latency, and processing costs. Native permissions and APIs may also make actions more reliable than loosely connected third-party integrations.

The role of temporary controls connects this development directly to Dell’Oro Group’s Network Security research. Firewalls, web application firewalls, workload controls, and other enforcement points could increasingly provide machine-generated shielding while application teams develop and validate permanent fixes. Microsoft demonstrated this type of workflow through custom detections, posture changes, application protections, and proposed code remediation.

Microsoft is not alone in pursuing this strategy. Palo Alto Networks is connecting security operations, cloud security, application security, agent orchestration, and network enforcement. CrowdStrike is building agentic workflows around its security operations platform and third-party ecosystem. Google can combine security operations, threat intelligence, cloud security, vulnerability research, and developer tools. Each vendor wants its platform to become the place where agents obtain context, make decisions, and coordinate action.

Agentic security could therefore accelerate security platform consolidation. Customers may prefer agents that arrive with preassembled context, tested tools, and established permission models rather than having to build cross-vendor workflows themselves. Vendors with broad telemetry and enforcement portfolios may also be able to improve their agents through operational feedback across more customers and use cases.

However, most large enterprises will remain multivendor. They may use Microsoft identity and productivity tools, Palo Alto firewalls, CrowdStrike’s endpoint platform, Google Wiz for cloud, and specialized products for application or data security. An agent that reasons accurately only inside its own vendor’s environment will provide an incomplete view of risk.

This challenge is particularly relevant to Dell’Oro Group’s AI & Cloud-native Security research, where risk context and enforcement are already distributed across cloud configurations, identities, workloads, application pipelines, and third-party security platforms. Agentic systems may improve how those signals are correlated and acted upon, but they do not eliminate the need to normalize data and coordinate controls across heterogeneous environments.

Microsoft acknowledged that third-party data quality, normalization, permissions, and enforcement remain difficult. Security data is inconsistent, customers frequently limit centralized ingestion because of cost, and external products expose different control mechanisms. Microsoft is exploring approaches such as data federation, but Perception’s practical openness will need to be demonstrated in customer environments.

The same test applies to competing platforms. Supporting connectors or open agent protocols does not by itself create reliable interoperability. Vendors must demonstrate that agents can interpret external evidence correctly, preserve source attribution, respect permissions, and execute actions without losing the safeguards available inside native products.

Openness also applies to models. Microsoft is pursuing a multi-model architecture but expects to certify supported configurations rather than permit unrestricted model substitution. That approach can improve quality and accountability, although customers may require different models because of sovereignty, cost, availability, or organizational policy. Platforms will need to balance customer choice against the risks created by untested combinations.

The market is approaching a practical contest between integrated performance and ecosystem reach. Broad platforms should have an advantage when their native products already dominate the customer environment. Openness will matter more as agents depend on external data sources and attempt to act across competing control planes.

Perception makes Microsoft’s platform opportunity visible, but it also sharpens the requirement for neutrality. Agentic security cannot become an enterprise operating layer unless it works across the enterprise that actually exists. The strongest platforms will not merely offer the largest collection of native agents. They will combine deep integration with credible operation across competing products.